Unconsulting in Cohorts
Become measurably safer together
In a cohort, several organizations implement the same security topic at the same time, each on its own systems. With a fixed rhythm, experienced experts and peers who face the same questions.
- Measurable progress in 6 to 12 weeks
- Proven with mid-sized companies and municipalities
- Exchange with peers on equal footing

The risks are known. Still, too little gets done.
Mid-sized companies and municipalities are attacked regularly, often successfully. Knowledge is rarely what's missing. What's missing is time, staff and budget.
In many organizations, IT security depends on one or two people. Audit reports reliably show them where the gaps are. Nobody tells them where to start.
Traditional consulting only helps so much: it is expensive, often delivers documents instead of implementation, and the knowledge leaves the building with the consultants.

Continuing risk

Scarce resources

Expensive one-to-one consulting
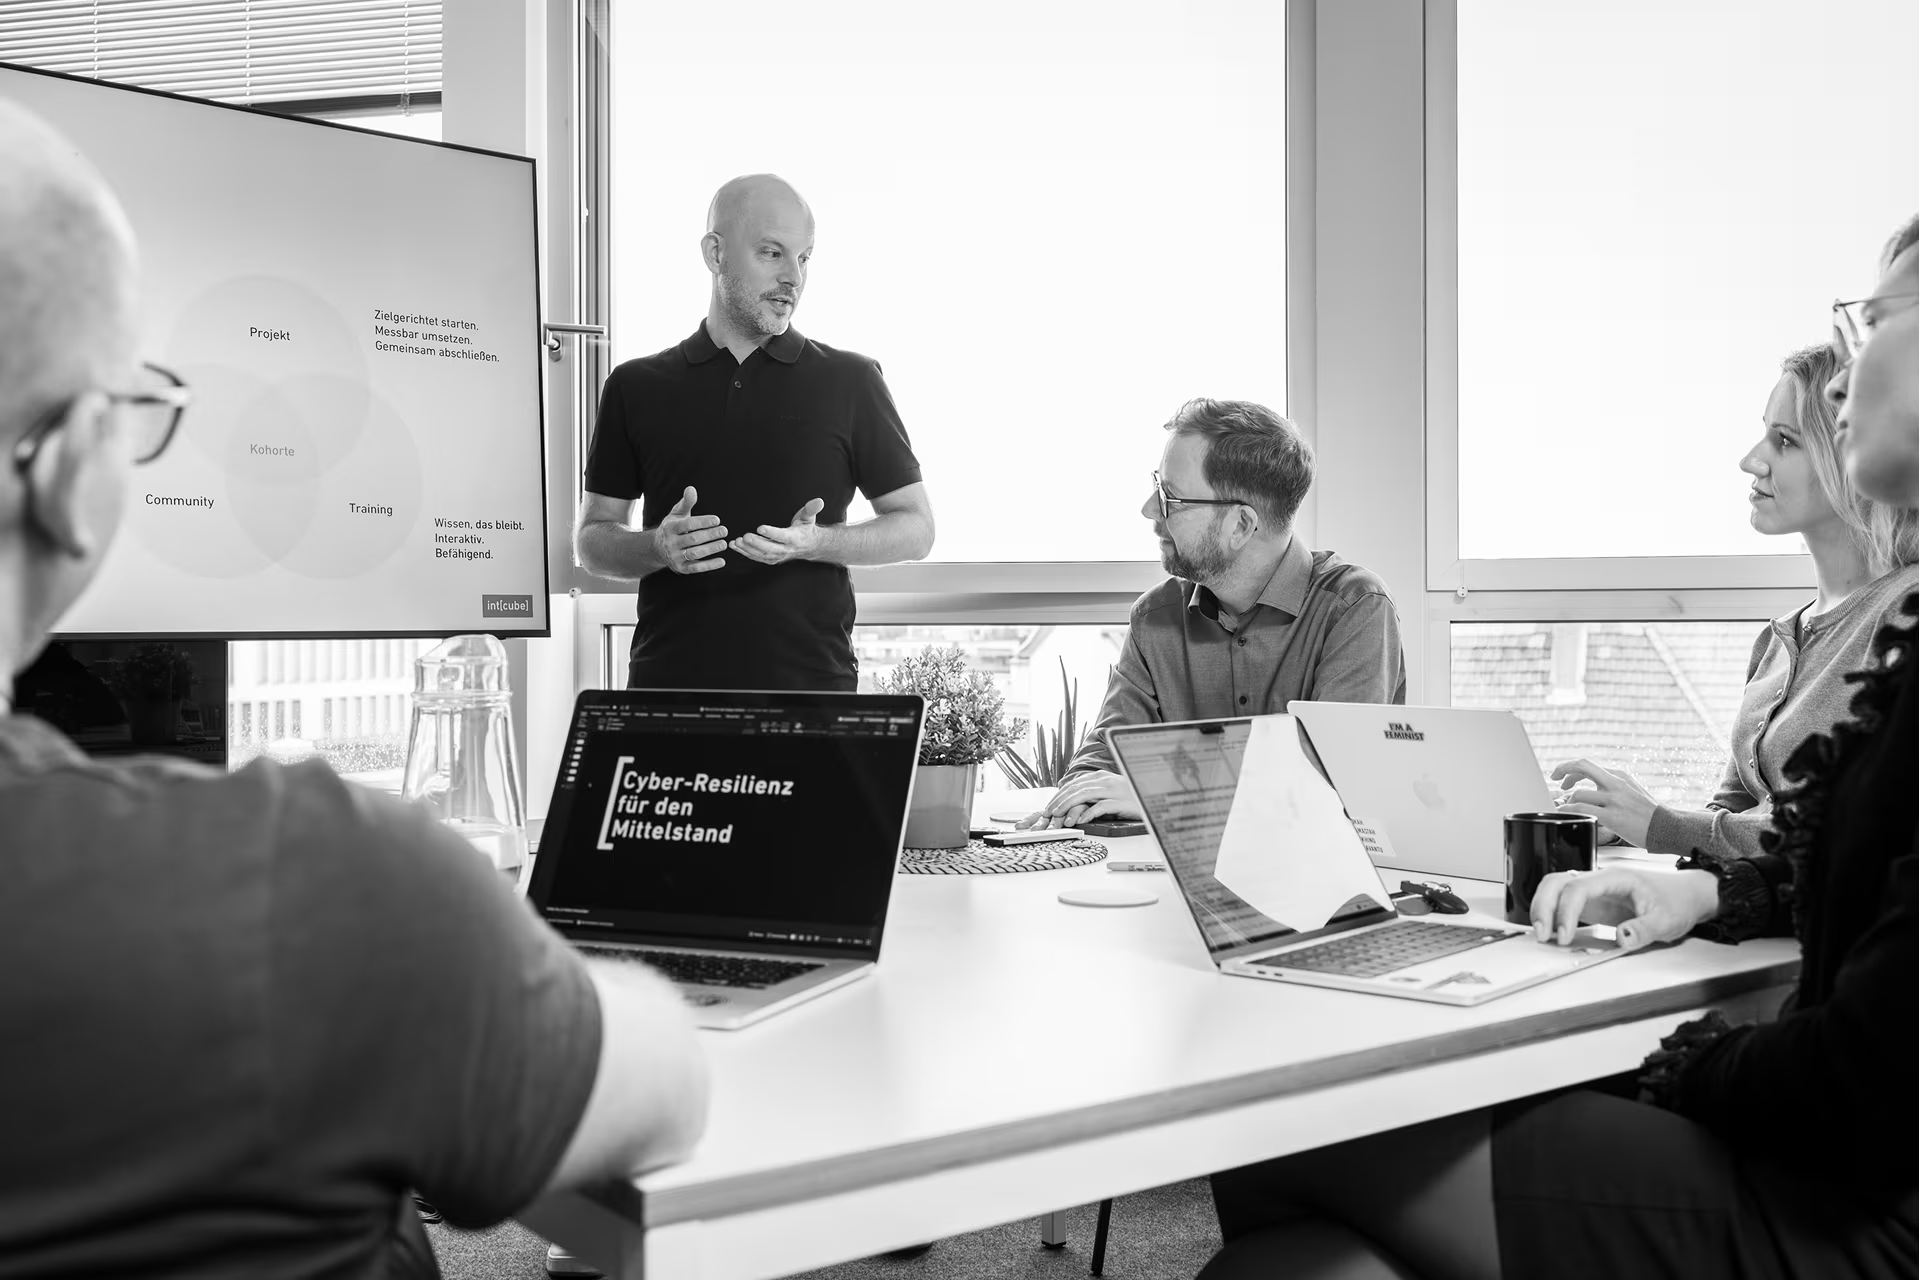
One task, many organizations, one shared roadmap.
In our cohorts, a group of organizations works on a clearly defined security topic at the same time. Each one implements it on its own systems. What they share: the method, templates, scripts, expertise and the exchange with each other.
The result: what each organization would otherwise buy on its own is created once and works for all of them. The experts' time is shared across the group. The documentation is finished when the cohort ends. And the knowledge stays with your own team.
A cohort combines the best of three worlds:
- Project: a clear goal, a fixed time frame, a shared finish
- Training: knowledge that stays, because it is built directly on your own systems
- Community: exchange on equal footing with people who have the same task
Unconsulting is built on the principles of the Unconsultancy Manifesto : impact at scale, organicity, transparency. How we apply it: Unconsulting at int[cube]
With cohorts at int[cube]

Measurable results
e.g. -68% external attack surface in 8 weeks

Clear structure
Structured roadmap with start, goal & concrete progress

Knowledge building
Empower your own team instead of buying advice

Resource efficiency
¼ to ⅔ of the cost of a consulting project

Peer networking
Exchange & joint learning in the cohort
Strengthen your cybersecurity with cohorts: structured, supported and measurable progress towards greater resilience.
Find focus
In cohorts, we focus on one topic (Attack Surface Management, Incident Response Readiness or NIS-2 Quick Wins) to make real progress.
Group exchange
In a cohort of organizations, everyone works on the same topic. You can share experiences and best practices with peers.
Clear framework
We provide a clearly defined time frame (depending on the topic, usually 6-12 weeks) and the matching tasks, so you can focus on the actual work.
Expert support
Our experts guide you through the cohort in weekly meetings and are available for questions and knowledge transfer.
Opt for real progress.
Better cybersecurity together: it motivates, it works and it delivers measurable results.
27
municipalities in the Lower Rhine region
hardened their Windows servers and Active Directory together. In 12 sessions, with KRZN as the coordinating partner. 100% of respondents would take part again.
Our experience: It's better together
With more than 20 years of experience in the IT security industry, we at int[cube] are convinced:
A resilient digital landscape comes from sharing knowledge and collegial exchange. Build a resilient organization and protect yourself.
With cohorts from
- reduce the risk of a successful attack
- achieve measurably better results with a clear roadmap
- empower your team for the long term instead of buying advice
- save significantly compared to traditional consulting
- connect with like-minded people
Don't take unnecessary risks.
Book a conversation with David Fuhr and find out how you can measurably improve your cybersecurity with cohorts in 6 to 12 weeks.

Questions in advance? Write to us!
David Fuhr
Founding Partner and CTO