Sell-Side Cyber Due Diligence for M&A

Know the findings before buyers find them

We assess your company’s cybersecurity from the buyer’s point of view before the sale process starts, and deliver a report and a dashboard for the data room.

  • Report in 2 to 3 weeks
  • Scorecard dashboard for the data room
  • Support in buyer Q&A
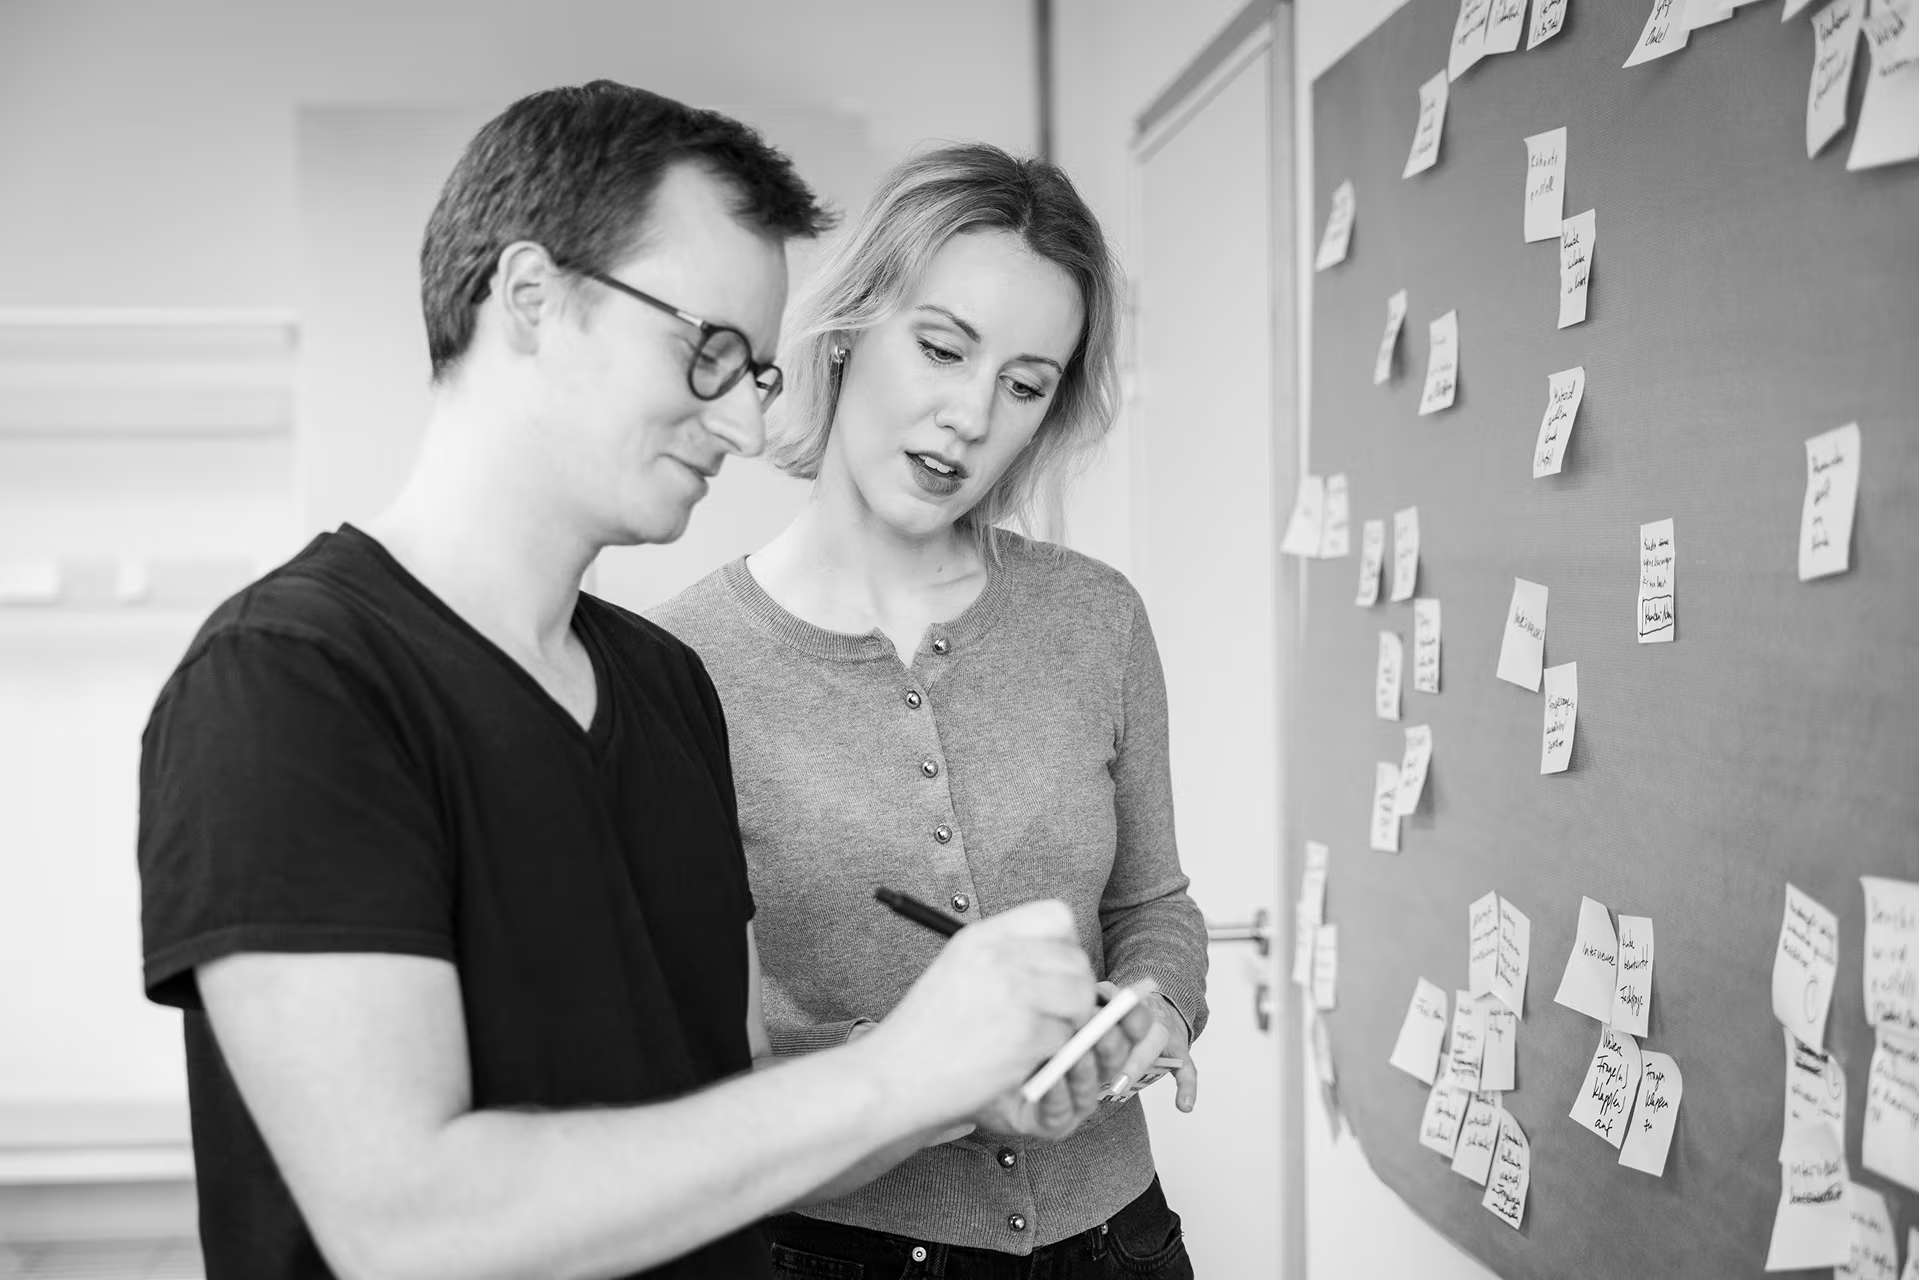
Two intcube team members in a workshop with sticky notes on the wall

In short: A sell-side cyber due diligence is an assessment of cybersecurity from the buyer’s point of view that you, as the seller, commission before the sale process. In two to three weeks we deliver a report and a scorecard dashboard for the data room, so you know and frame the findings before bidders find them.

Duration
2 to 3 weeks
Result
Sell-side report, scorecard dashboard for the data room, support in buyer Q&A
Contact
David Fuhr

In a sale process, buyers decide what is said about your cybersecurity.

When several bidders find the same weaknesses one after another, each becomes a negotiation point: for price reductions, indemnities or exclusions in the W&I insurance. Data-room questions multiply, and the timetable comes under pressure.

With a sell-side cyber due diligence you know the state beforehand: what is good, what is a real risk, what fixing it costs. Quick improvements happen before the launch; the remaining points you frame yourself, with a plan.

We assess the way buyers would, with the experience of more than 50 buy-side due diligence projects.

  • Findings as negotiation points

  • Many questions from many bidders

  • Pressure on price and timetable

Know the state and frame it yourself

Which findings would a buyer’s due diligence produce today? Which are real risks, which only missing evidence? What can still be closed before the process starts? And how do you present the rest with a credible plan?

We deliver the answers in two to three weeks and then support you in the Q&A with bidders.

With int[cube]'s sell-side cyber due diligence:

Buyer-view assessment

Governance, identities, attack surface, product security, backups and past incidents, as in a buyer’s DD

Cyber Value Scorecard

Exposure, control maturity and remediation effort per area, as a dashboard for the data room

Sell-side report

Findings with context, remediation costs and a plan

Quick improvements

What can still be closed before the sale process starts, ranked by effect.

Q&A support

We answer bidders’ cybersecurity questions based on the report and dashboard.

A report that makes the sale process calmer.

Fast

Report and dashboard in two to three weeks, so the sale timetable holds.

01

Buyer view

We know the buy side’s questions from more than 50 due diligence projects of our own.

01

Data-driven

The scorecard makes the state comparable and traceable, also for several bidders at once.

01

Start before the sale process.

Enhance your cybersecurity now

Keep control of the story

We assess your cybersecurity from the buyer’s view and deliver a report that brings clarity to the data room.

Resources for deal teams

Cyber Due Diligence Checklist for Private Equity Deals: a practical checklist covering governance, identity, external attack surface, product security, data protection, incident response, third-party risk, backups, and the post-close 100-day plan. Use it before signing.

The Cyber Resilience Act for private equity: who is affected, the 24-hour reporting duty since September 2026, the December 2027 deadline and what to check in due diligence.

‍

With int[cube] as a partner

  • Know the findings before bidders do
  • Close quick gaps before the launch
  • Frame open points yourself, with a plan
  • Answer bidders’ questions from one source

Frequently asked questions

What is a sell-side cyber due diligence?

An assessment of cybersecurity from the buyer’s point of view, commissioned by the seller before the sale process. The result, a report and a scorecard dashboard, goes into the data room and answers bidders’ questions from one source.

When is a sell-side cyber due diligence worth it?

In sale processes with several bidders, for technology-driven companies where cybersecurity affects the price, and whenever past incidents or known gaps need explaining.

How long does it take?

Two to three weeks to report and dashboard. After that, we support the Q&A with bidders.

What do we get as a result?

A sell-side report with findings, context, remediation costs and a plan, a scorecard dashboard for the data room and support with bidders’ questions.

How is it different from exit readiness?

Sell-side cyber due diligence documents the state for buyers. Exit readiness improves cybersecurity in the roughly twelve months before. Combining both means going into the sale in the best shape.

How does it fit into the investment lifecycle?

It is the last of seven steps; on the buyer’s side, the next cycle starts with it. The whole sequence is on cybersecurity for private equity firms.

Note: this page and our services are not legal advice. We align contract clauses, warranties, indemnities and insurance questions with your legal counsel.

Sell with a clear picture

Book a conversation with David Fuhr and learn how a sell-side cyber due diligence protects your sale process.

Book a call now

Questions in advance? Write to us!

David Fuhr

Founding Partner and CTO